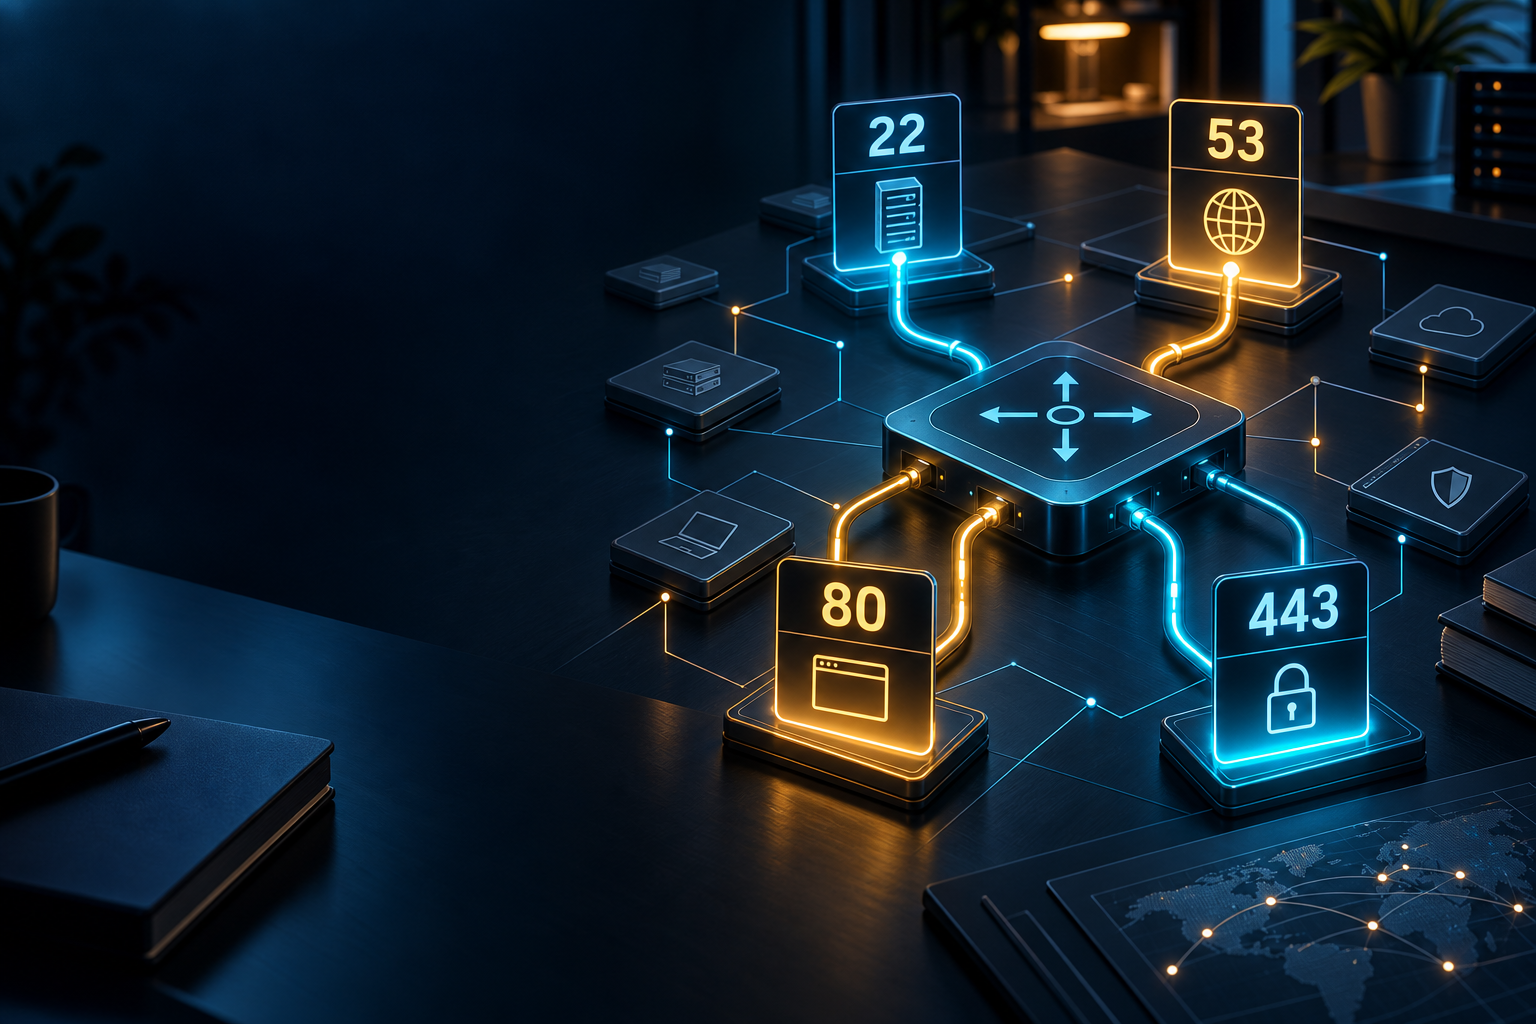
Group ports by function, pair insecure services with their protected alternatives, and practise retrieving the number from the service name. Network+ is the closest CompTIA match for this topic because its N10-009 objectives explicitly list common ports. A+ Core 1 also tests ports and protocols, while Security+ applies port knowledge to secure protocol selection and defensive scenarios.
Click to load the YouTube player. Watch on YouTube ↗
- 01Network+ N10-009 contains a dedicated common ports, protocols and services objective.
- 02A+ Core 1 includes a networking ports and protocols objective, but its exam scope is broader IT support.
- 03Security+ SY0-701 expects secure communication, open-service and hardening context rather than one official fixed list.
- 04Port numbers are clues, not proof. Confirm the protocol, transport, host role and traffic behaviour.
- 05The free guide below adds plain-English service explanations, memory cues, security notes and an OSI model reference.
Why the exact number still matters
On the job, you can look up a port in seconds. During an exam or a live incident, instant recognition still saves time. A firewall event on 3389 suggests a remote desktop conversation. A DNS query normally points to 53. A connection to 23 raises a different question from one to 22 because Telnet and SSH have very different security expectations.
A port is not an identity card. IANA registers service names and transport assignments, but a service can run on a non-default port and a registered port does not prove what traffic is actually present. Treat the number as a lead, then validate the protocol, source, destination, timing and asset role.
Network+ is the cleanest title match for this article: objective 1.4 explicitly asks candidates to explain common networking ports, protocols, services and traffic types. A+ Core 1 also names a useful subset under Networking, including FTP, SSH, Telnet, SMTP, DNS, DHCP, HTTP, POP3, IMAP, LDAP, HTTPS, SMB and RDP. Security+ names open service ports, secure protocol selection and port selection inside broader security objectives, so use port knowledge as part of a defensive decision rather than treating a memorisation list as the whole exam.
The list, chunked by job
Study the columns by function rather than reading from 1 to 22. The first pass is recognition. The second pass asks what the service does. The third asks what a defender should check.
How this approach helped me pass Security+ first time within 28 days
When I started studying cybersecurity seriously, I did not come from a formal cybersecurity background. I had practical exposure to MFA, IAM and cloud security while building web and mobile apps, including work around Google Cloud and Firebase controls, but I had never studied cybersecurity in a structured way.
One area I kept getting caught out on in practice questions was network ports. I could remember some, forget others and lose confidence when a long list of numbers appeared without context. I used AI tools to help organise a study guide in a way my brain could digest, then kept testing myself against it. Within 28 days, I passed Security+ on my first attempt.
That is my personal learning story, not a promise that another learner can reproduce the same result. The useful part was the method: the guide connected the port number, protocol, service name, plain-English purpose, memory cue and security note. Understanding why a service mattered made recall much easier than repeating a number in isolation. I also added an OSI model reference so the guide supported broader networking understanding.
Four techniques that hold up under pressure
1. Chunk before you memorise
Use small families: web, email, remote access, file transfer, naming and infrastructure. Working memory handles meaningful groups better than a flat list of unrelated numbers.
2. Anchor protected services to risky neighbours
Pair 80 with 443, 23 with 22, 110 with 995, 143 with 993 and 389 with 636. Then remember the important exception: SFTP is a separate SSH-based protocol, while FTPS adds TLS to FTP.
3. Build your own memory cues
Use a cue that means something to you. For example, 80 is the web page your browser “ate,” while 3389 becomes a distinctive remote desktop rhythm. Your own image is usually more useful than borrowing a mnemonic that does not connect to anything you know.
4. Quiz yourself instead of rereading
Cover the port column and recall the number from the service name. Then reverse the quiz. Research on testing-enhanced learning finds that retrieving information can improve delayed retention more than repeated study alone, so spread short retrieval sessions across several days.
Know the number, explain the service, connect the security consequence, then retrieve it again tomorrow.
Self-check before exam day
Give yourself one point for each item you can answer without looking. Six out of six is a useful check for this guide’s subset, not proof that you are ready for an entire certification exam.
Want the reference guide?
Get the DirtyPhish Network Ports and OSI Model Reference Guide. It turns each number into a service, a plain-English explanation, a memory cue and a security note.
This is an independently written study aid, not official CompTIA exam material.Practise the pressure
Use the article for understanding, then use a game to practise retrieval and decisions without a lookup.
 PRIMARY PRACTICE
 NETWORK DEFENCE
 SOC CONTEXT
Ports, protocols and exam prep
Which CompTIA exam is most closely matched to a common ports guide?+
Network+ is the closest match because its N10-009 objectives explicitly list common ports, protocols and services. A+ Core 1 also includes a defined ports and protocols objective, while Security+ uses ports in secure protocol selection, open-service and hardening scenarios.
Do I need to memorise every port in the IANA registry?+
No. IANA registers thousands of service names and ports. Use the high-yield set in this guide as a practical study list, then follow the current CompTIA objectives for the exam you are taking.
Are TCP and UDP ports numbered differently?+
They have separate transport-layer namespaces, so the same number can be assigned independently to TCP and UDP services. DNS commonly uses UDP 53, but TCP 53 is also used for larger or special exchanges.
Is SFTP the same thing as FTPS?+
No. SFTP is a file-transfer protocol carried over SSH, normally port 22. FTPS is FTP secured with TLS and uses FTP conventions rather than the SSH protocol.
How many ports should I know before an exam?+
There is no official universal 25-port CompTIA checklist. Learn the ports named in the current objectives, understand what each service does, and practise recalling them under time pressure.
Sources and scope
- CompTIA Network+ N10-009 exam objectives, especially objective 1.4.
- CompTIA Security+ SY0-701 exam objectives, including open service ports and secure protocol selection.
- CompTIA A+ Core 1 exam objectives, including the ports and protocols objective. Exam codes and objectives can change, so confirm the current version before studying.
- IANA Service Name and Transport Protocol Port Number Registry.
- RFC 8314 for implicit TLS and STARTTLS email submission guidance.
- Roediger and Karpicke, Test-Enhanced Learning for the retrieval-practice note.
This is an independently written educational guide. It is not official CompTIA exam content, does not reproduce exam questions and cannot guarantee a pass result.