SOC alert triage is the fast first assessment of a security alert. Analysts or automation validate the signal, remove duplicates, add context, judge severity and business impact, then close, monitor or escalate it. The goal is not to investigate everything. It is to keep a genuine incident from disappearing inside a queue of low-value noise.
Click to load the YouTube player. Watch on YouTube ↗
- 01Triage separates false positives, expected behaviour and genuinely suspicious activity.
- 02Context from users, assets, endpoints, cloud systems and threat intelligence changes priority.
- 03Severity describes technical danger; priority also considers asset value, exposure and business impact.
- 04Every disposition should improve tomorrow's detections through tuning and documented feedback.
- 05AI can speed enrichment and grouping, but accountable human review still matters for ambiguous cases.
The problem alert triage exists to solve
Alert volumes vary by organisation, tooling and detection maturity, so any universal average should be treated carefully. The consistent pattern is more important: security teams receive far more signals than they can investigate with equal depth, and a large share are duplicates, expected behaviour or false positives.
An Osterman Research survey reported that close to 90% of participating security operations centres described themselves as overwhelmed by false positives and backlogs. Industry figures for false-positive rates vary widely, often from 50% to 90%. The variation is a warning against treating one percentage as a benchmark, but it also explains why a deliberate triage process is essential.
Find the small number of alerts that can hurt the organisation before the size of the queue hides them.
The SOC alert triage process, step by step
- 01CollectAlerts arrive from SIEM, EDR, email, identity, cloud and network controls.
- 02Validate and deduplicateCheck whether the alert is genuine, already represented by another case or generated by a known noisy rule.
- 03EnrichAdd user, asset, process, location, history and threat-intelligence context.
- 04Score severity and priorityCombine technical risk with asset criticality, exposure and likely business impact.
- 05Dispose or escalateClose expected activity, monitor uncertain activity or send a credible threat to deeper investigation.
- 06Feed backRecord the outcome and tune detections so the same noise does not consume the same effort tomorrow.
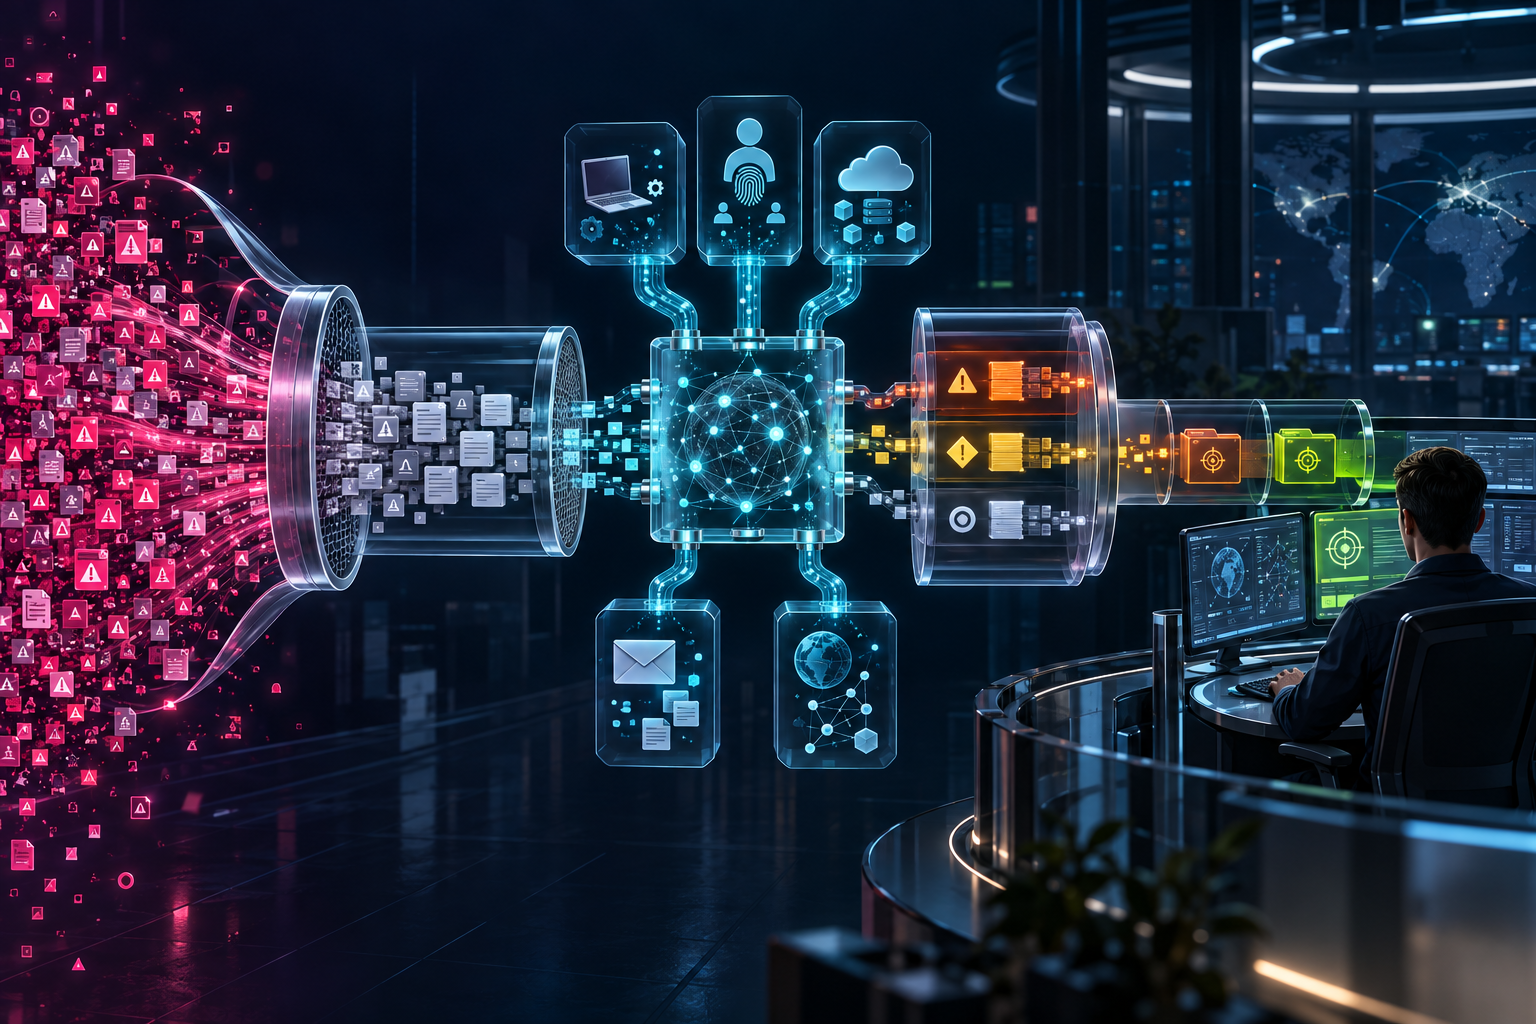
Where the alert volume goes
The target is not an impressive suppression percentage by itself. A small team can still be flooded by a low percentage of a huge total. Useful measures include how many alerts analysts touch, how long high-priority alerts wait and whether genuinely malicious activity is being missed.
How SOC analysts decide what comes first
Credential dumping and destructive commands normally carry more inherent danger than a routine policy violation.
The same suspicious login matters differently on a test device and on a domain controller or production cloud administrator.
Corroborating endpoint, identity and network evidence raises confidence beyond one isolated rule firing.
Exposure, data sensitivity, privileged access and active business processes help determine urgency.
Segmentation also changes the answer. A compromised endpoint with unrestricted access to backups and servers creates a different priority from an endpoint isolated inside a tightly controlled zone. See what network segmentation means for the blast-radius side of that decision.
Where AI fits in the SOC in 2026
AI-assisted triage is useful when it reduces repetitive work. It can pull context from several systems, group related alerts into one case, draft a timeline and classify familiar benign patterns consistently. Those tasks give analysts more time for novel or ambiguous activity.
It is not a reason to remove scrutiny. Elastic Security Labs described a production triage experiment in which an agent working only from an alert's immediate context reached roughly 60% accuracy, and analysts found enough inaccurate summaries that they stopped relying on them. Later designs improved when the system could use richer historical case context. The practical lesson is to test against real outcomes, measure errors and keep a human able to challenge or override the result.
AI can collect and organise evidence. The organisation still needs a defensible decision, a documented reason and a person responsible for high-impact escalation.
Common triage mistakes
- Every alert is treated as urgentEqual attention sounds safe but delays the alerts whose technical severity and business impact are genuinely highest.
- No feedback reaches detectionsClosing a false positive without tuning the rule guarantees the same work returns.
- AI summaries are trusted blindlyA fluent explanation can still be wrong. High-impact cases need evidence checks and an override path.
- Only percentages are measuredA tolerable false-positive percentage can still create an impossible absolute queue for a small team.
- Asset context is missingA detection without identity, device role and business value cannot be prioritised consistently.
Practise SOC judgement under pressure
These games turn triage, evidence correlation and risk prioritisation into fast, visible decisions.
 PRIMARY PRACTICE
 EVIDENCE CORRELATION
 RISK PRIORITY
Questions people ask
Is alert triage the same job as being a SOC analyst?+
Triage is a core responsibility for many Tier 1 SOC analysts, but it is a process rather than the entire job. Depending on the SOC, automation, AI tools, managed providers and human analysts may all perform parts of it.
What is the difference between triage and a full incident investigation?+
Triage is the fast initial decision about whether an alert needs deeper attention and how urgently. A full investigation establishes scope, root cause, impact and remediation after triage has justified the extra time.
Can a small business triage alerts without a dedicated SOC?+
Yes. Smaller organisations often use a managed detection and response provider because building a staffed in-house SOC is not practical. The validation, enrichment, prioritisation and escalation workflow remains broadly the same.
Why must alert dispositions feed back into detection rules?+
Without feedback, the same noisy rule continues to create the same false positives. Tuning based on actual outcomes is one of the few actions that reduces tomorrow's workload rather than only clearing today's queue.
Can AI remove humans from SOC alert triage?+
Current evidence does not support removing human judgement entirely. AI is useful for enrichment, grouping and repetitive classification, but ambiguous, novel or high-impact cases still need accountable human review and an override path.