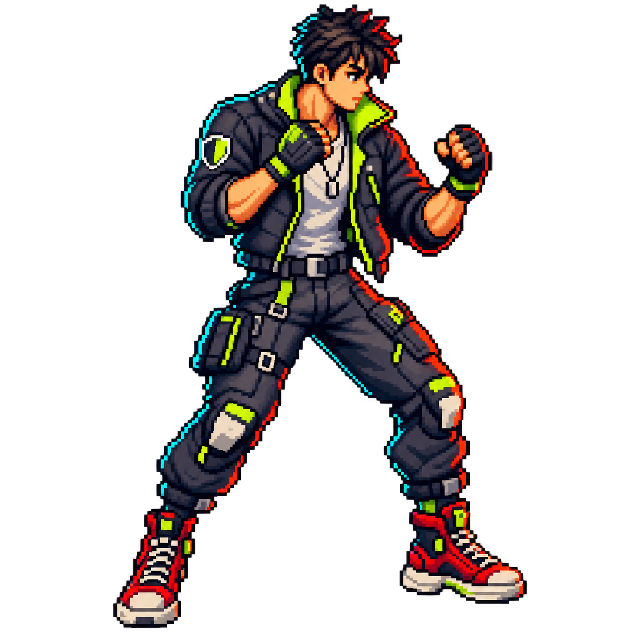
 PLAYER 01
PATCH
Fast hands. Strong firewall.
THE NEON BREACH
KEYBOARD: MOVE WASD / ARROWS · PUNCH J · KICK K · BURST L
Fight through five escalating sectors, keep PATCH on their feet, and stop DirtyPhish before the final breach. Chain jabs into hooks and uppercuts, read enemy wind-ups and control each crowded lane with keyboard or touch controls.
Hooded breach runners now jab, lunge, flank and throw hostile data packets instead of causing damage by simply touching PATCH. Read their warning signal, move out of the lane, build your Firewall Burst meter, then break through to the angler behind the operation.
PLAYER 01Fast hands. Strong firewall.
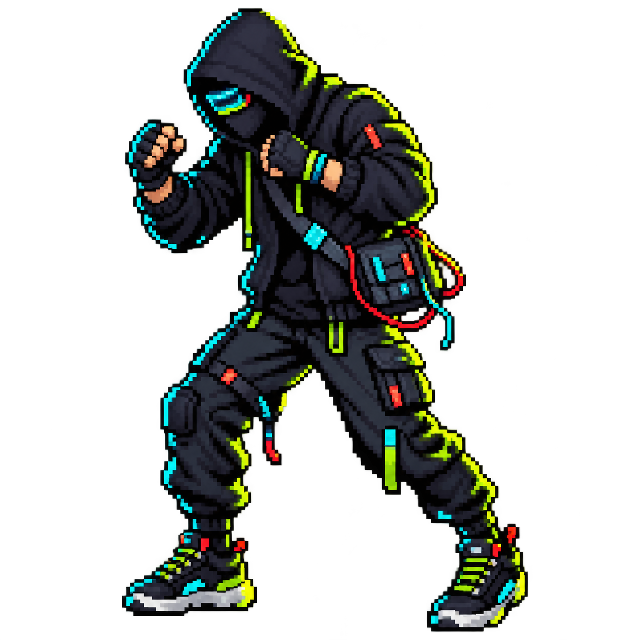 THREAT CLASS
Cheap tricks. Dangerous in packs.
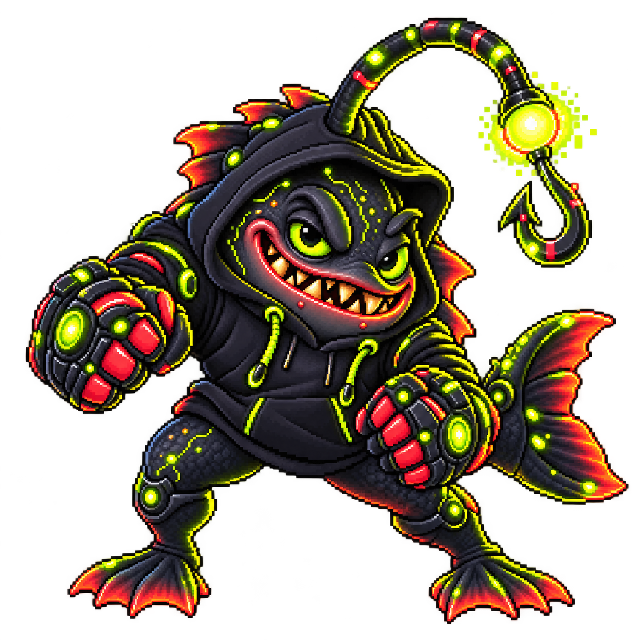 FINAL BOSS
Big lure. Bigger health bar.
Press repeatedly to chain a jab into a hook, then finish with a wide uppercut that can catch several nearby enemies.
Chain a front kick, roundhouse and crowd-clearing sweep. Each hit adds reach, damage and knockback.
When the meter is full, release a 360-degree blast that hits every nearby threat.
Firewall Fury turns network defence into an arcade metaphor. PATCH protects a neon network, breach runners represent hostile activity, and the Firewall Burst represents a defensive control stopping threats before they spread. Real cybersecurity is less theatrical, but the central idea is accurate: defenders reduce risk by controlling access, watching traffic, fixing weaknesses and responding quickly when something unusual happens.
A network firewall examines connections and applies rules that decide which traffic may pass. It can separate the public internet from a private network, restrict communication between internal zones, block unwanted services and record activity for investigation. A firewall does not automatically know whether every permitted action is safe, so clear rules and regular review matter.
Network services communicate through agreed protocols and ports. Web browsing commonly uses HTTPS, email uses its own protocols, and remote administration uses others. Security teams reduce exposure by allowing only the services a system genuinely needs. An unnecessary open port is like an unused arcade entrance left unlocked.
Network segmentation divides devices and services into controlled zones. Staff laptops, guest Wi-Fi, payment systems and critical servers should not all have unrestricted access to one another. If one device is compromised, segmentation can limit lateral movement and stop a small incident becoming a network-wide breach.
A security patch repairs a known weakness in software or firmware. Attackers often scan widely for systems that have missed important updates. Effective patch management means knowing what assets exist, prioritising serious flaws, testing changes and installing updates promptly rather than waiting until an exploit is already spreading.
Malware is software designed to steal, spy, disrupt or provide unauthorised access. A botnet is a group of compromised devices controlled together, sometimes for spam, credential attacks or distributed denial-of-service activity. Endpoint protection, secure configuration, patching and network monitoring help detect and contain these threats.
DirtyPhish represents phishing and social engineering: messages that imitate trusted people or services to steal credentials or trigger unsafe actions. Defend accounts with unique passwords, a password manager and multi-factor authentication. Verify unexpected payment, password or file-sharing requests through a separate trusted channel.
A firewall is valuable, but it cannot replace secure identities, well-configured devices or alert people. Defence in depth combines preventive, detective and recovery controls so that one missed attack does not decide the whole outcome. Least privilege limits what each account can reach; logging and intrusion detection reveal suspicious behaviour; protected backups support recovery; and a rehearsed incident-response plan helps teams contain damage.
This is also why Firewall Fury gives PATCH movement, attacks and a special meter instead of a single unbeatable button. In real networks, prevention, detection and response must work together. Organisations should test those layers regularly and improve them after incidents, exercises and changes to their technology.
A firewall allows, blocks or records network traffic according to security rules. It creates a controlled boundary between devices or network zones, but it must be configured and maintained to stay useful.
No. Permitted traffic can still carry phishing, stolen-account activity or malicious files. Strong defence also needs current software, multi-factor authentication, endpoint security, monitoring, backups and people who know how to report suspicious activity.
A firewall controls network connections. Antivirus or endpoint detection examines files, processes and behaviour on a device. They solve different problems and are normally used together as part of layered security.
Segmentation separates a network into smaller zones with controlled connections. It reduces unnecessary access and makes it harder for malware or an intruder to move from an ordinary device to sensitive systems.
Change default router credentials, install firmware updates, use modern Wi-Fi encryption, choose unique passwords, enable multi-factor authentication, remove unused devices and treat unexpected links or login requests with caution.