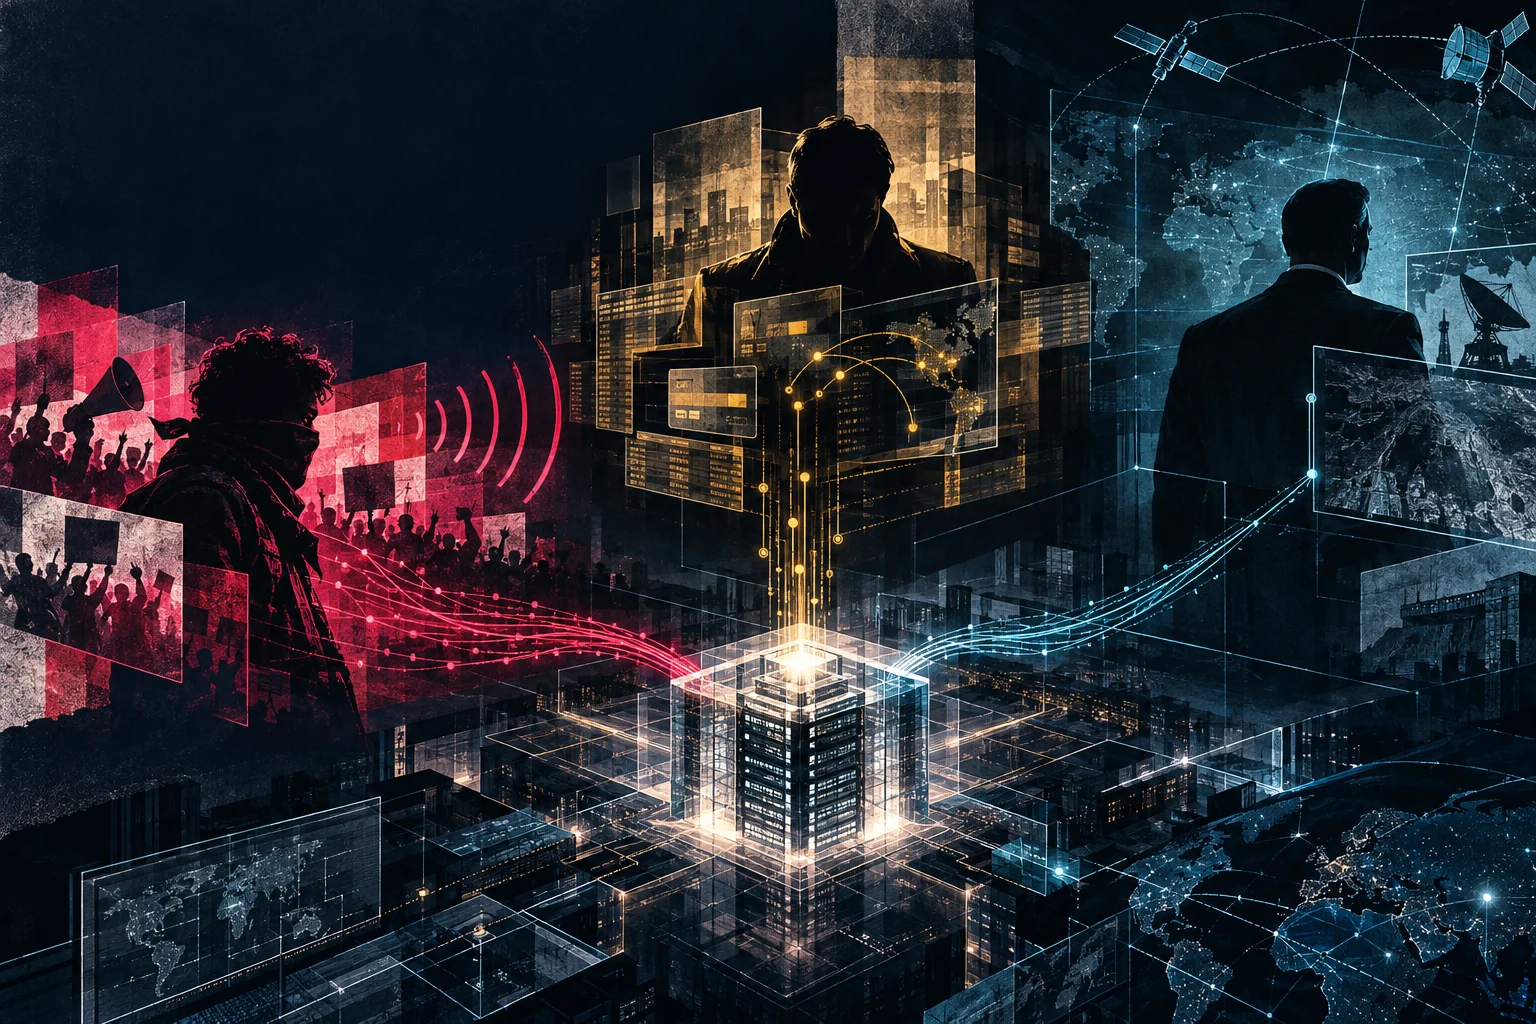
Motive is the fastest useful distinction. A hacktivist wants attention for a cause. A cybercriminal wants financial gain. A nation-state actor wants strategic advantage. The difficult part is that groups may borrow one another's tools, branding and access, so defenders must classify behaviour from evidence rather than trusting the name an attacker uses.
Click to load the YouTube player. Watch on YouTube ↗
- 01Hacktivists prioritise visibility, disruption and an ideological message.
- 02Cybercriminals prioritise profit through theft, fraud, ransomware or extortion.
- 03Nation-state operators prioritise espionage, strategic access or pre-positioning.
- 04Similar tactics do not prove that two groups have the same motive or sponsor.
- 05Attribution should remain a confidence-based assessment, not a dramatic guess.
The three, side by side
Threat-actor labels are useful because motive influences target selection, patience, publicity and the way access is monetised. They are starting points for an investigation, not proof by themselves.
Hacktivist: an attack that wants an audience
A hacktivist is primarily motivated by a political, social or ideological cause. Visible techniques such as website defacement, denial-of-service activity and public data leaks can support that aim because disruption and attention are part of the intended effect.
Capability varies widely. Some groups depend on simple, reusable tools, while others demonstrate coordination or access that suggests support from better-resourced partners. Public claims should therefore be treated as evidence to evaluate, not automatic proof of responsibility.
Cybercriminal: quiet until profit requires noise
A cybercriminal is primarily motivated by money. The operation may remain quiet while credentials, data or access information is collected. It becomes visible when the attacker needs to demand payment, sell stolen data or pressure a victim into a ransom negotiation.
Modern financially motivated operations frequently begin with identity compromise rather than an obvious malware attachment. Phishing, stolen session tokens, help-desk impersonation and access purchased from another criminal can all provide the first foothold. That is why identity, endpoint, help-desk and network evidence must be examined together.
Nation-state actor: access built for patience
A nation-state actor works for, or on behalf of, a government. The objective may be espionage, strategic positioning, intellectual-property collection or maintaining the option to disrupt critical services later.
These operations tend to value continued access over immediate profit. Attribution can take time because researchers must combine infrastructure, tooling, targeting patterns and behaviour. A strategically important target and long dwell time may raise suspicion, but neither clue proves state sponsorship independently.
Where the categories overlap
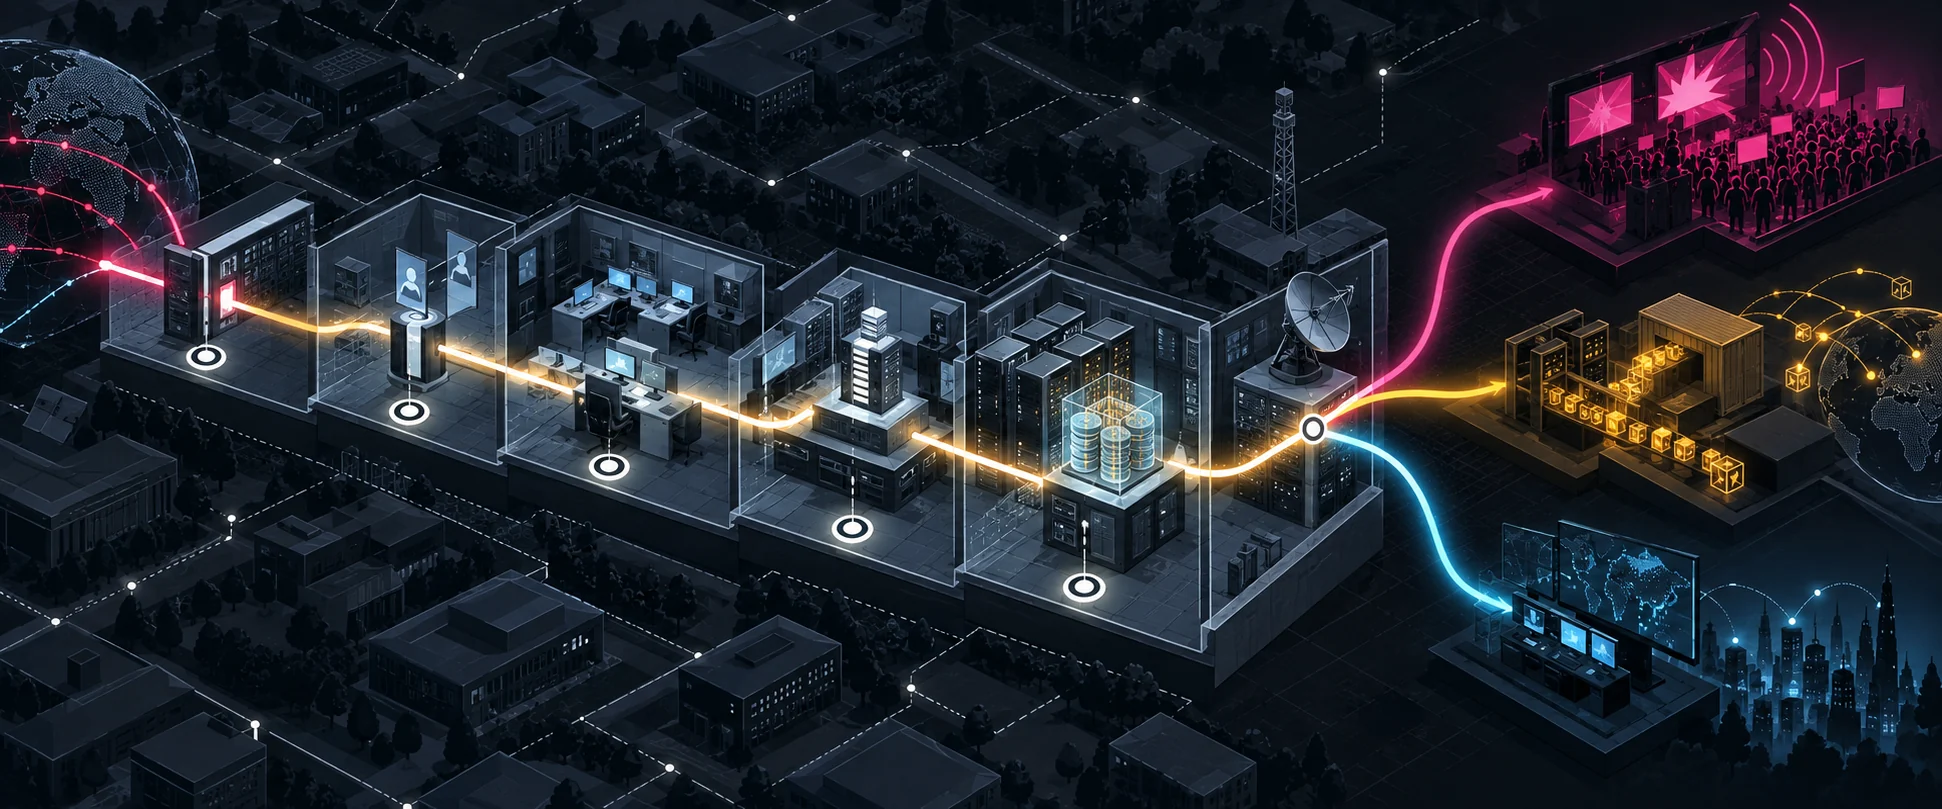
The boundaries blur when a state-aligned group adopts hacktivist branding, an ideological collective uses ransomware to fund itself or a criminal affiliate uses access originally obtained by another actor. Plausible deniability makes those overlaps useful to attackers.
Separate motive, capability and affiliation. A group's public identity may indicate motive, but it does not prove skill level, sponsorship or who originally provided the access.
A useful assessment therefore describes confidence: what is known, what is inferred and what evidence would change the conclusion. That discipline matters more than forcing every incident into a perfectly clean label.
Why classification matters to defenders
If an incident appears ideologically motivated, public communications and resilience against visible disruption may become urgent. If financial crime is likely, preserve evidence, prepare for extortion and investigate how access might be monetised. If strategic espionage is plausible, widen the investigation, assume a longer dwell time and look carefully for persistence beyond the first affected system.
Classification does not replace containment. Defenders still need to protect accounts, isolate affected systems and preserve evidence. It helps the response team anticipate what the attacker may do next and which evidence deserves immediate attention.
Practise identifying the adversary
These four games approach the same problem from different angles: motive, ethics, connected evidence and incident response.
 PRIMARY PRACTICE
 ETHICS + INTENT
 EVIDENCE MAPPING
 INCIDENT RESPONSE
Questions people ask
Can one group be more than one type of threat actor?+
Yes. A group can begin with an ideological motive, adopt financially motivated tactics and still receive direction or protection from a state. Treat the categories as descriptions of the dominant motive and relationship at a given time, not permanent identities.
Are hacktivist attacks genuinely dangerous?+
They can be. Some claims are exaggerated, but denial-of-service attacks, destructive activity and leaked sensitive information can still create serious operational and reputational harm.
Why are nation-state actors difficult to prosecute?+
They normally operate outside the target country's jurisdiction and may have government protection. Responses are therefore more likely to involve public attribution, sanctions or diplomatic action.
How do researchers attribute an attack?+
Researchers combine technical evidence such as infrastructure and tooling with behavioural evidence such as targeting, monetisation, dwell time and actions taken after access. A single clue is rarely conclusive.
Does AI change the threat-actor categories?+
AI changes the cost and scale of operations more than the underlying motives. It can help less-resourced actors produce more convincing messages and process information faster, but the defensive questions remain focused on intent, access and behaviour.