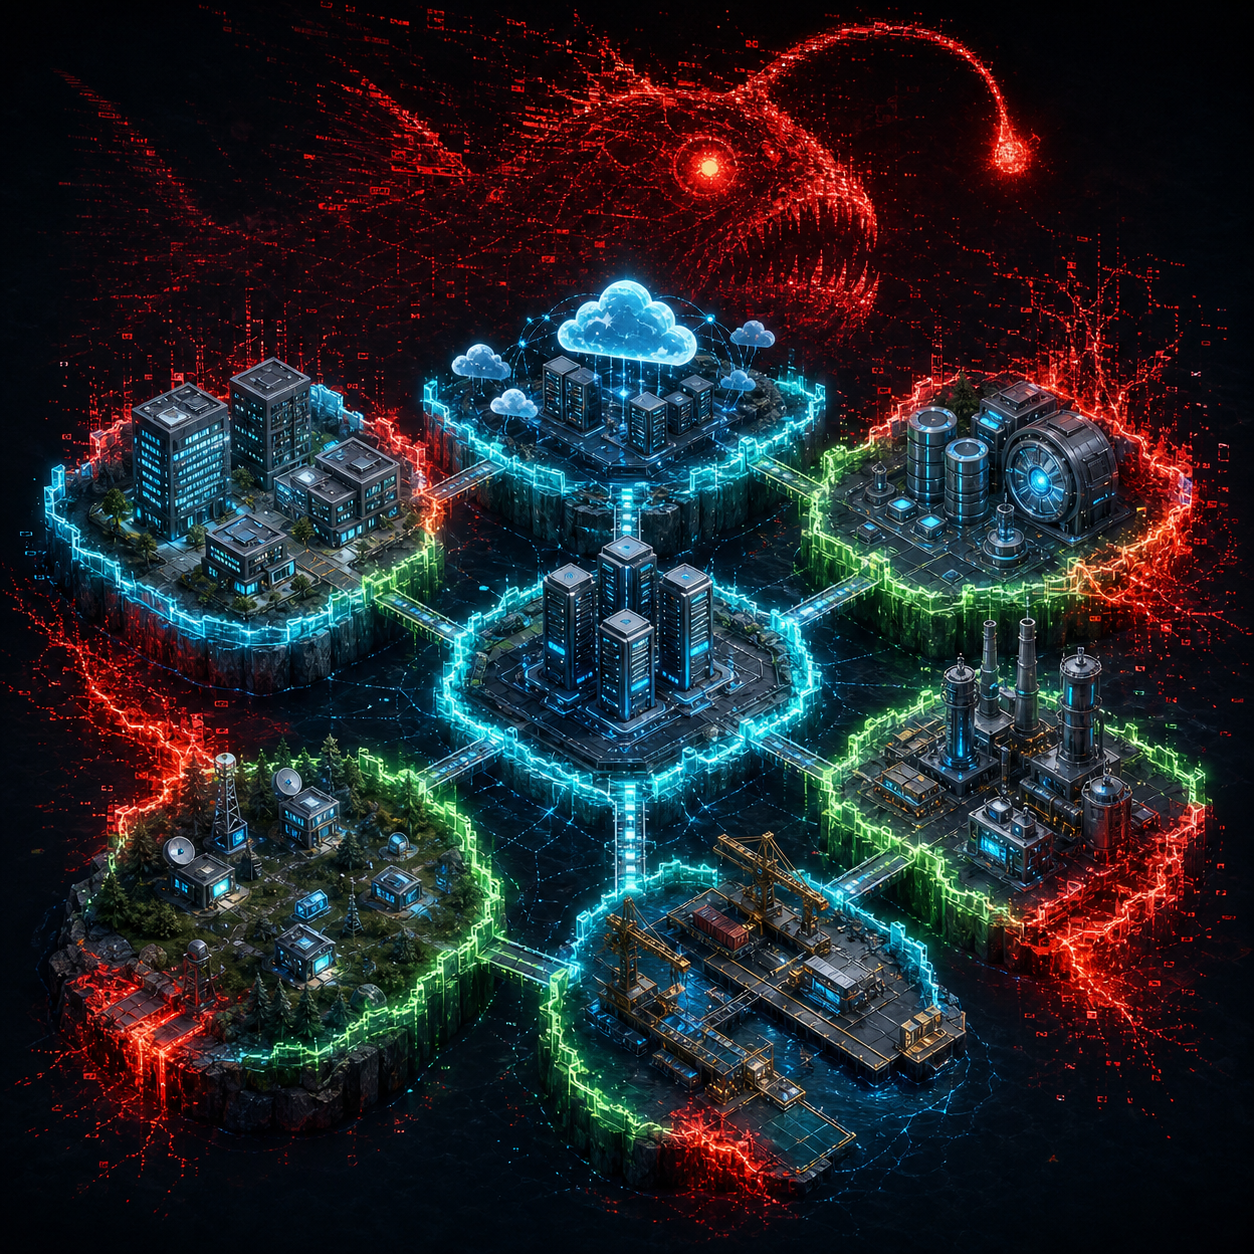
How do you contain ransomware across a corporate network?
Start by identifying and isolating affected systems. Protect clean segments, revoke compromised access, prioritise actively exploited weaknesses and recover from clean, tested backups only when the environment is ready. CISA advises organisations to immediately isolate impacted systems and notes that segmentation can limit lateral movement.
Use your approved incident response plan in a real event. Patch Dominion is an educational simulation, not an operational playbook.
Read the CISA StopRansomware Guide ↗CONTROL 01 // SEGMENTLimit trusted paths
Segmentation separates business units and technology zones with controlled traffic rules. In the game, isolation stops spread immediately but reduces continuity. In practice, planned segmentation can restrict lateral movement before an incident begins.
CONTROL 02 // PRIORITISEPatch risk, not noise
A long vulnerability list does not tell you what to fix first. Combine active exploitation, external exposure, asset importance and likely impact. CISA's Known Exploited Vulnerabilities Catalog is one useful input for risk-based remediation.
CONTROL 03 // DETECTDeploy endpoint protection
Endpoint detection and response can identify suspicious behaviour, contain activity and give responders evidence. It is not guaranteed protection, which is why the game treats EDR as a strong probability rather than an invincibility shield.
CONTROL 04 // IDENTITYBlock compromised access
Cloud accounts, email systems, remote workers and suppliers depend heavily on identity. Revoking tokens, disabling risky accounts and strengthening authentication can close routes that malware controls alone may miss.
CONTROL 05 // RECOVERRestore clean backups
Backups support recovery only when they are protected, monitored and tested. The UK NCSC recommends regular backups of important files and checking that restoration works as expected. Recovery does not replace containment.
CONTROL 06 // CONTINUITYAccept the right disruption
Emergency isolation can protect the wider organisation, but critical services may be interrupted. Good response planning defines who can make that decision, which services must be preserved and how teams communicate during the event.
How should vulnerabilities be prioritised?
Prioritise vulnerabilities that attackers are actively exploiting, especially when they affect internet-facing or business-critical systems. Then consider exposure, available mitigations, asset value and operational constraints. A severe score alone does not describe the full risk.
The game represents those factors with territory risk, attack paths and limited security credits. Protecting a high-risk database can matter more than patching several low-impact endpoints.
Explore the CISA KEV Catalog ↗PATCH DOMINION QUESTIONS
What is Patch Dominion?
Patch Dominion is a free daily cybersecurity strategy game. You defend a corporate network by patching systems, isolating segments, deploying endpoint protection, blocking risky accounts and restoring clean backups before an outbreak spreads.
How do you contain ransomware on a network?
Identify affected systems, isolate them quickly, protect clean segments, revoke compromised access, preserve evidence and restore from tested clean backups under an approved incident response plan. Exact actions depend on the incident and organisation.
What is network segmentation?
Network segmentation divides an environment into controlled zones. Rules between zones limit unnecessary traffic and trusted paths, which can restrict lateral movement and reduce the number of systems reached by an intruder.
How should security teams prioritise patches?
Prioritise weaknesses that are actively exploited, reachable by attackers and present on critical assets. CISA recommends using its Known Exploited Vulnerabilities Catalog as an input to risk-based vulnerability prioritisation.
Why does isolating a system affect business continuity?
Taking a device, account or network segment offline can stop an attack from spreading, but it can also interrupt legitimate work. Incident response teams balance rapid containment with safety, critical services and operational impact.
Are backups enough to stop ransomware?
No. Backups support recovery, but they do not stop initial access, credential theft or lateral movement. Organisations also need prevention, detection, containment and tested restoration procedures.
Is the daily Patch Dominion map the same for everyone?
Yes. The game uses the current UTC date to create the same outbreak and opening positions for every player that day, which makes scores directly comparable.
Is Patch Dominion a Territorial.io clone?
No. Patch Dominion is an original cybersecurity learning game built around incident containment. It takes broad inspiration from fast territory-control strategy games but uses its own map, controls, scoring, artwork and security mechanics.
Does Patch Dominion work on mobile?
Yes. Every territory and response control supports touch input, and the command map adapts to phone, tablet and desktop screens.